Fintech executive leadership
Fintech CTO Consulting: Resilience, Controls and Scale
Hire a fintech CTO with a clear mandate for payment correctness, resilience, controls and scale. Use operating scenarios and a practical first-phase scorecard.
- By
- Fractional CTO Experts
- Published
- 2026-07-30
- Reviewed
- 2026-09-07
- Reading time
- 14 minutes
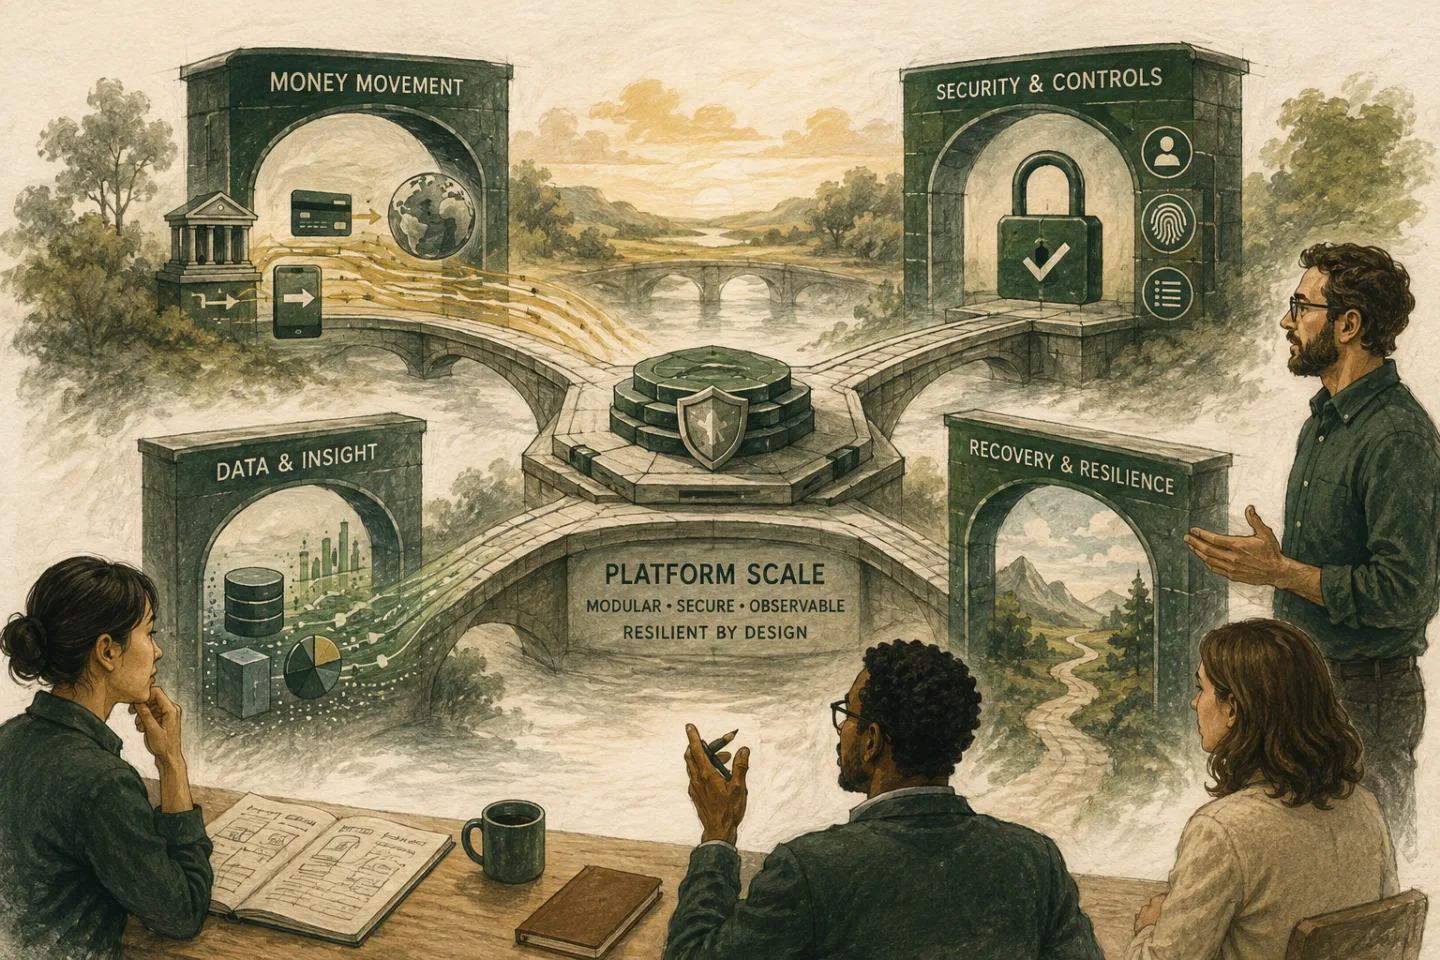
Fintech technology leadership has to hold two truths at once: the company must change fast enough to find and grow a market, and systems handling money, identity, sensitive data, or regulated workflows must remain explainable and dependable.
A strong CTO does not treat compliance as a document team or security as a final review. They connect business exposure, product behavior, platform architecture, operating controls, evidence, and recovery.
- Map technology failure to customer harm
- Build resilience as an operating capability
- Turn controls into evidence
- Protect correctness while scaling
- Govern vendors and partners
- Define a bounded fractional mandate
- Select with operating scenarios
- Measure leadership in business terms
- Start with the product's responsibility boundary
- Design explicitly for an ambiguous payment result
- Make reconciliation a product capability
- Test recovery against a meaningful disruption scenario
- Turn assurance requests into an evidence backlog
- Scope the first ninety days around decisions
- Decide when fractional leadership is insufficient
- Make the board conversation decision-ready
Map technology failure to customer harm
Start with what can go wrong for customers and the business:
- money is moved twice, not moved, or moved to the wrong destination;
- balances or statements become inconsistent;
- an unauthorized person gains access;
- a service outage blocks time-critical activity;
- a dependency fails or changes behavior;
- reconciliation cannot explain differences;
- sensitive data is exposed or used outside its purpose;
- fraud controls block legitimate users or miss abuse;
- a regulatory or partner obligation cannot be evidenced;
- an incident is detected late or communicated poorly.
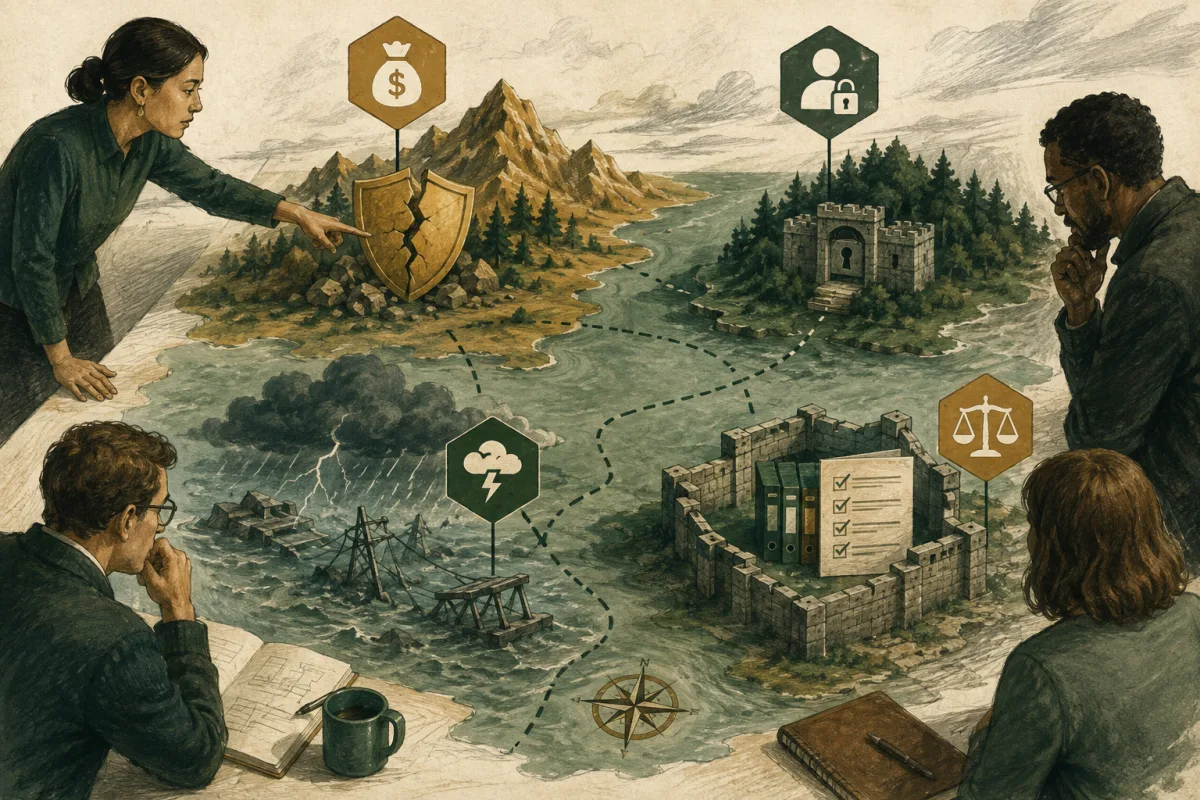
This mapping gives architecture and control discussions a business frame. It also prevents a company from applying equal effort to every theoretical weakness.
Build resilience as an operating capability
Resilience is not one redundant database. It combines prevention, detection, containment, recovery, communication, and learning.
For critical journeys, define:
- service and recovery objectives tied to user impact;
- dependency and failure-mode assumptions;
- observability that detects customer harm, not only server health;
- safe degradation, queuing, limits, and manual operations;
- incident authority and communication routes;
- backup and recovery tests;
- vendor contingency;
- post-incident learning with owned changes.
Interview CTO candidates about a failure they personally led. Look for how they made decisions, involved risk and business stakeholders, communicated uncertainty, protected customers, and changed the system afterward.
Turn controls into evidence
A policy is a statement of intent. An operating control needs:
- an owner;
- a defined action and frequency;
- evidence that the action occurred;
- exception detection and escalation;
- review when the system or risk changes.
The CTO should work with qualified legal, compliance, risk, audit, and security specialists to identify obligations. Technology leadership translates those obligations into system behavior, ownership, change processes, and evidence. It should not offer legal conclusions outside its competence.
Avoid building a “compliance platform” disconnected from how teams work. Evidence collection that depends on heroic quarterly screenshots is a signal that controls are not integrated.
Protect correctness while scaling
Fintech scale is not only transactions per second. It is the ability to preserve correctness, traceability, limits, recovery, and cost as volume and product complexity increase.
Important patterns may include:
- explicit ledger and balance ownership;
- idempotent operations and duplicate handling;
- limits, state transitions, and authorization;
- immutable event or audit evidence where appropriate;
- reconciliation across internal and external systems;
- data lineage and versioned business rules;
- controlled change and rollback;
- capacity and failure testing;
- customer-impact monitoring;
- clear exception operations.
The correct architecture depends on the product. Do not demand a bank-grade internal ledger from a product that never holds or represents balances. Do not rely on a processor’s correctness where the company still owns user state and reconciliation.
Govern vendors and partners
Fintech products often depend on banks, processors, identity providers, data sources, cloud services, card networks, and compliance tooling. The CTO should make the operating boundary visible:
- Which party owns each decision and failure?
- What evidence and service commitments exist?
- How are changes announced and tested?
- What happens during vendor degradation?
- Can data be exported and reconciled?
- Which concentration and exit risks are accepted?
- Who manages support escalation?
Vendor certification does not transfer accountability for the customer experience.
Define a bounded fractional mandate
Useful fractional or interim assignments include:
- assess platform readiness before licensing, partnership, or enterprise expansion;
- build a resilience and incident program;
- clarify architecture and investment before scale;
- establish security and control evidence;
- recover delivery while protecting change governance;
- lead technical diligence or post-acquisition planning;
- bridge a CTO departure;
- design the permanent leadership role.
The mandate should state the jurisdiction, product model, licenses or partners, customer type, transaction flows, current team, business event, and required specialist support.
Select with operating scenarios
Ask:
- A payment provider returns an ambiguous timeout. What must the product know and do?
- Reconciliation differences increase after a release. How do you contain and investigate?
- An enterprise prospect requests security evidence the company does not have. What happens next?
- Growth requires a new region with different partners and data constraints. Which decisions come first?
- A control passes audit but creates repeated production risk. Who can change it?
- A critical vendor is degraded during peak volume. What is the customer and operating plan?
Good answers expose assumptions and stakeholder roles. They do not jump straight to a tool. Ask for the candidate’s comparable personal decisions and references.
Measure leadership in business terms
A first-phase scorecard could include:
- critical customer journeys and risks mapped;
- service, recovery, and incident ownership agreed;
- control owners and evidence gaps visible;
- reconciliation and data truth clarified;
- architecture and vendor concentration decisions sequenced;
- delivery and change risk measured;
- board and partner reporting improved;
- team and leadership gaps addressed;
- a funded 90-day and 12-month roadmap.
Do not claim that one executive makes a company compliant or secure. Measure whether risk decisions are visible, evidence exists, operations can respond, and the organization can support the product promises it makes.
Start with the product's responsibility boundary
“Fintech” is not one operating model. A budgeting application, a payment orchestration service, a lending platform and software used by a regulated institution expose customers to different failures. Before selecting a CTO or commissioning an architecture review, draw the actual product boundary. Identify who holds funds, who records the authoritative balance, who makes eligibility decisions, who processes identity data and who communicates a failed transaction to the customer.
Then follow one representative customer journey across that boundary. A mobile interface may show a single transfer while the service depends on your application, a processor, a banking partner and a notification provider. The CTO needs to understand which state belongs to each party and how disagreements are detected. Outsourcing part of the flow can reduce implementation work, but it does not automatically remove your responsibility for the claims your product makes.
| Product situation | First technical question | Specialist input to establish |
|---|---|---|
| Personal finance aggregation | How fresh and complete is the imported data? | Data-use permissions and customer disclosures |
| Payment initiation | What does pending, completed or failed mean across parties? | Payment and partner obligations |
| Lending workflow | Can the decision and its inputs be reconstructed? | Credit, legal and model-governance requirements |
| Card payment acceptance | Which systems encounter payment account data? | Applicable PCI scope and assessment approach |
| Infrastructure sold to a financial institution | Which critical operation depends on the service? | Contractual, resilience and assurance requirements |
This table is an interview framework, not a determination of regulatory status. Record unresolved questions and assign them to the appropriate risk, compliance, legal or security specialist. A CTO who confidently assigns every obligation from a product label is skipping the evidence that makes the answer useful.
Design explicitly for an ambiguous payment result
A timeout is a communication outcome, not proof that a payment failed. Consider an illustrative transfer request: the application sends a command to a provider, the provider accepts it, and the network connection fails before the application receives the response. If the product displays “failed” and invites a completely new transfer, it may create a duplicate instruction. If it displays “complete” without evidence, it may mislead the customer in the other direction.
A suitable design needs a durable identity for the requested operation, a defined intermediate state and a way to resolve uncertainty using the provider's supported mechanisms. The exact identifiers, retry rules and expiry behavior depend on the integration. The product team must decide what the customer sees while the state is unresolved, and operations must know when an unresolved item requires investigation. Engineering cannot solve the problem solely by increasing a request timeout.
In this example, an unresolved transfer remains visibly pending while the application checks authoritative state. Repeating an action must not silently create a second business operation. An operator can inspect the original request, provider reference and subsequent events without editing a balance directly. Resolution produces an auditable transition and, where necessary, a customer message explaining the outcome. This is a design scenario, not a universal implementation recipe for every payment network.
Webhook handling introduces another source of uncertainty. Stripe's webhook documentation explains that event order is not guaranteed and that events may be delivered more than once. It also describes signature verification. A CTO should ask how the integration authenticates events, handles repetition and determines the current business state instead of assuming that arrival order describes reality.
Questions that reveal actual operating experience
Ask a candidate to walk through the ambiguous request without a slide deck. Which fact is known at each step? Where is the operation identity created? What happens if a worker crashes after applying a change but before acknowledging the event? How does customer support explain the state? Which action could accidentally duplicate the payment? What evidence is preserved if the incident later becomes a dispute?
A strong answer will identify missing provider-specific details and resist pretending that one database transaction controls the entire external system. A weaker answer will name a queue or an idempotency key and stop before discussing customer state, operational recovery and reconciliation.
Make reconciliation a product capability
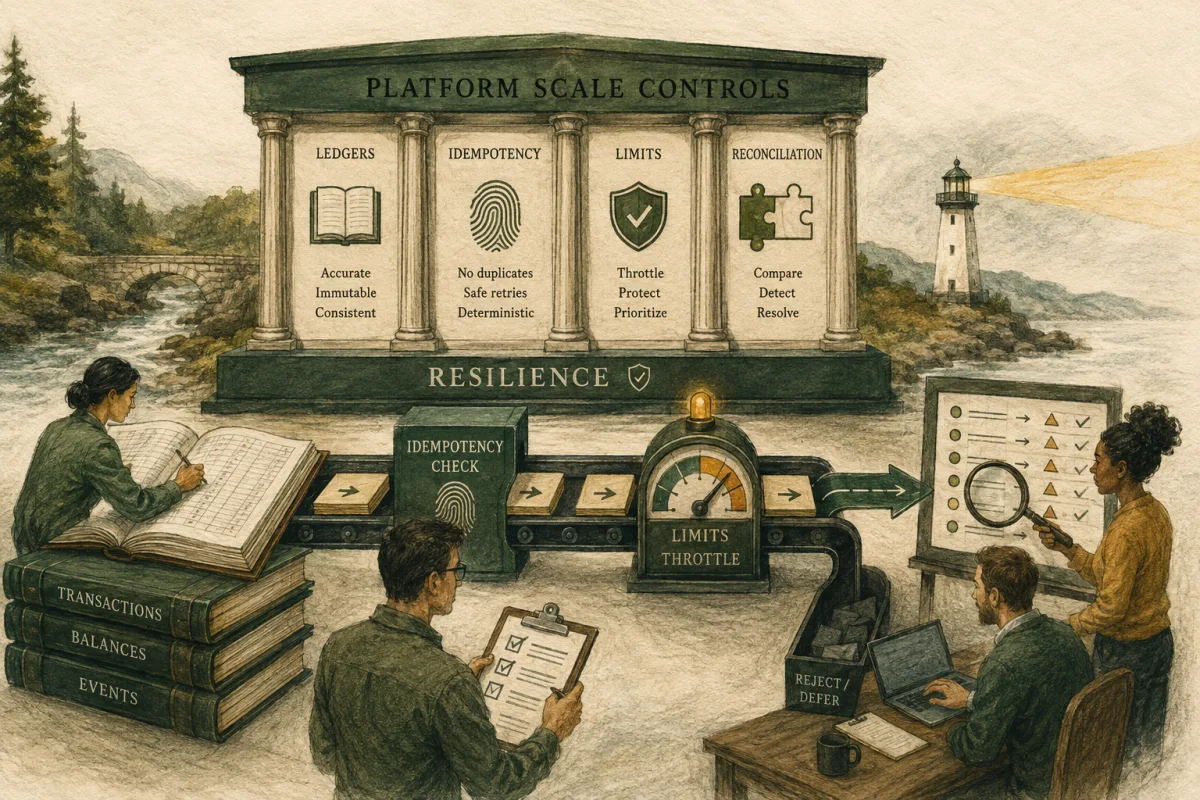
Reconciliation compares independent records and explains differences. It should have an owner, a schedule, a source of truth for each field and an exception workflow. A spreadsheet can be a reasonable early operating tool when access, review and change handling are controlled. It becomes dangerous when it is the only place where unresolved money movements are understood and no one can reconstruct how a correction was made.
For an illustrative daily review, suppose the internal application contains 1,000 submitted operations while a partner report contains 997 matching completions. The difference does not establish that three payments are lost. One may still be pending, one may have been rejected and one may have a mismatched reference. The useful work is to classify each discrepancy, establish the evidence and route it to a named owner. Posting an unexplained adjustment to make totals match destroys the signal you need to investigate.
Review both aggregate and item-level checks. Matching a total can hide offsetting errors. Likewise, item counts can match while amounts, currencies or beneficiaries differ. The appropriate checks follow the product's financial model and partner interfaces. Finance and operations should help define them; engineering should make them reproducible and observable.
A decision-ready exception record contains the business operation identifier, expected state, observed state, source timestamps, value at risk where relevant, assigned owner, current hypothesis and next action. Record when an exception was resolved and why. As volume grows, prioritize automation that reduces repeated manual classification without removing the ability to explain an unusual case.
Test recovery against a meaningful disruption scenario
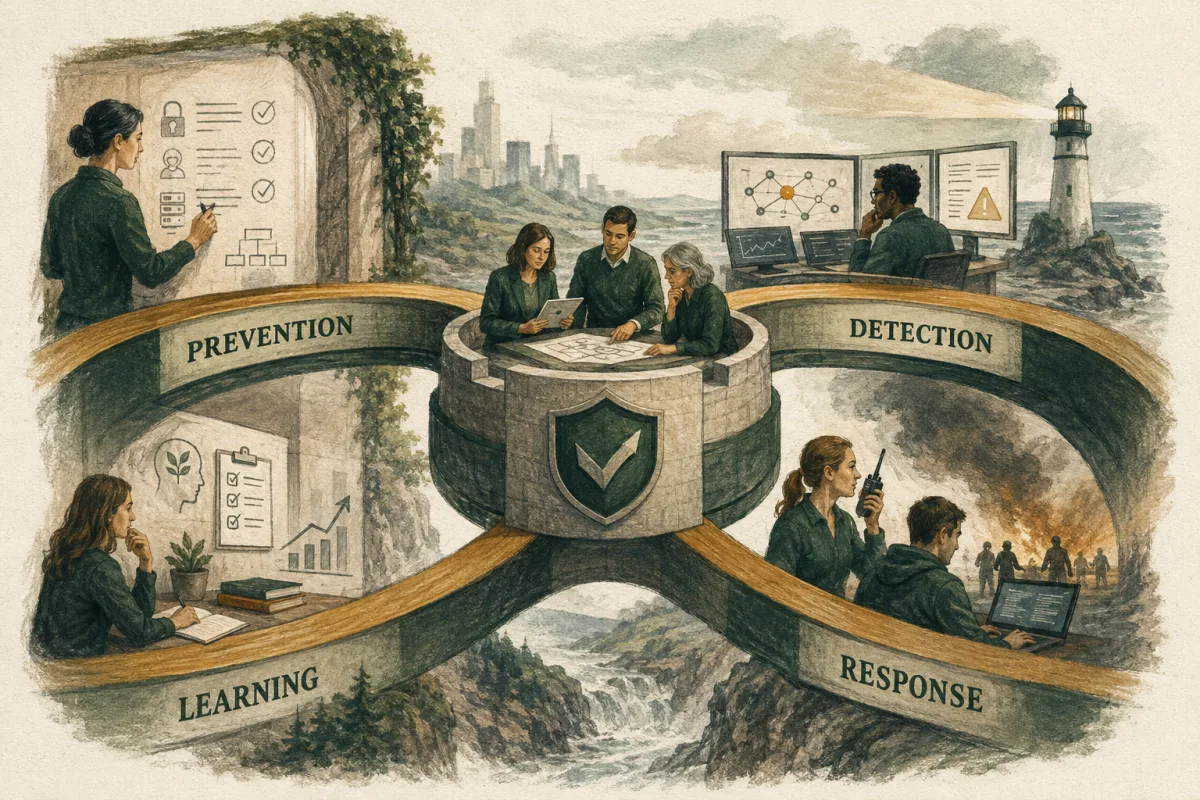
A recovery exercise should answer a business question, such as whether customers can obtain an accurate view of pending activity after a regional service interruption. A successful database restore is only one input. The team also needs to reconnect external state, verify access, identify events that arrived during the interruption and ensure that customer messages do not contradict the recovered records.
The Basel Committee's Principles for operational resilience address banks and emphasize maintaining critical operations through disruption. They can inform a discussion with banking partners; they do not establish that every fintech company is directly subject to the same framework. Establish the requirements applicable to your entity and contracts with qualified specialists.
Build a tabletop exercise around one concrete failure. A critical partner becomes unavailable during a busy period. The incident lead needs to decide whether to queue new requests, limit a product function or stop accepting a category of activity. Customer support needs approved language that reflects what is known. Finance needs to understand unsettled exposure. The partner relationship owner needs a route to escalation. The CTO coordinates the technical choices within the agreed authority structure.
After the exercise, capture decisions that could not be made because information or authority was missing. “Improve incident response” is not an actionable finding. “Name the person authorized to stop new transfers, provide a current view of pending operations and rehearse the customer-status update” gives the team specific work. Repeat the exercise after the relevant changes, rather than treating a completed meeting as proof of readiness.
Turn assurance requests into an evidence backlog
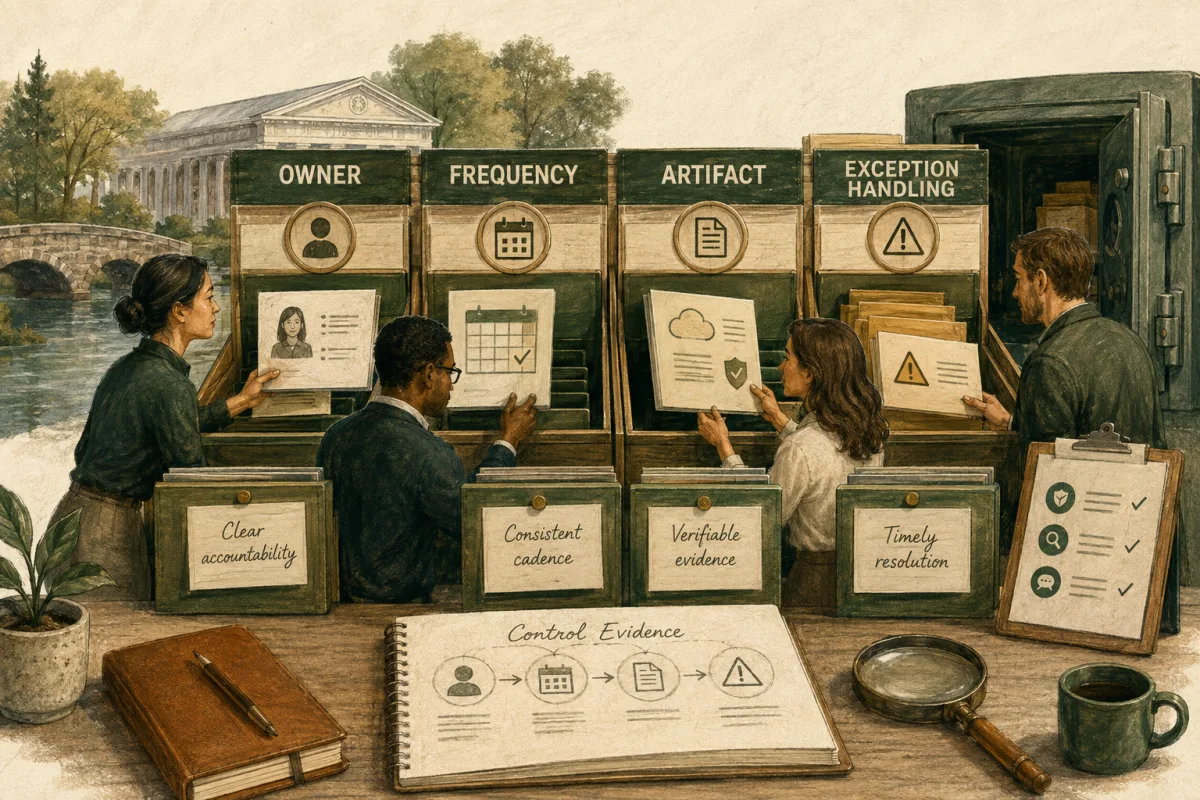
An enterprise prospect or banking partner may ask for policies, architecture information, access-control evidence, incident procedures and independent assurance. Route the request through an owner who can distinguish existing evidence, evidence that needs updating and controls that do not yet exist. Never answer “yes” to a control question because a document describes the intended future state.
For payment account data, use the PCI Security Standards Council document library to identify current official materials with the assessor or other qualified party responsible for your scope. A provider's validation and your own system boundary are separate questions. Avoid treating the purchase of a payment product as evidence that every part of your application is covered.
A practical evidence backlog connects each request to its system, owner, artifact, period covered and unresolved exception. A recent access review should show what was reviewed and what happened to exceptions. A recovery report should state the scenario actually tested and its limitations. The CTO's contribution is to make evidence collection a consequence of how the team operates, while specialists determine the adequacy of the evidence for the applicable obligation.
Prioritize the gaps according to customer harm, contractual commitments and the business decision at hand. A large folder of low-value documents can distract from an untested recovery path or unclear privileged access. Explain the tradeoff to the sponsor and obtain an explicit decision where a risk cannot be resolved immediately.
Scope the first ninety days around decisions
A fractional CTO engagement should begin with the evidence the company already has. Do not spend the first month rebuilding a document inventory merely because a template expects it. Agree which business event drives the work and which unresolved technology decisions prevent progress.
| Phase | Work to complete | Reviewable result |
|---|---|---|
| Initial assessment | Map critical journeys, responsibility boundaries and existing evidence | A shared view of material unknowns and immediate containment needs |
| Decision phase | Evaluate the highest-priority correctness, resilience and ownership gaps | Options with effort, dependencies, accountable owners and tradeoffs |
| Execution support | Help teams implement selected changes and rehearse operations | Evidence that the chosen controls and operating procedures work in the tested scenarios |
| Handover | Review remaining exposure, team capacity and leadership needs | A funded next plan with a clear ongoing decision owner |
The phases are a planning example, not a promise that every company can complete its risk work in ninety days. A transaction, licensing process or major remediation may change both duration and required expertise. State what the fractional leader can own, what the internal team must execute and which specialist decisions sit outside the engagement.
Decide when fractional leadership is insufficient
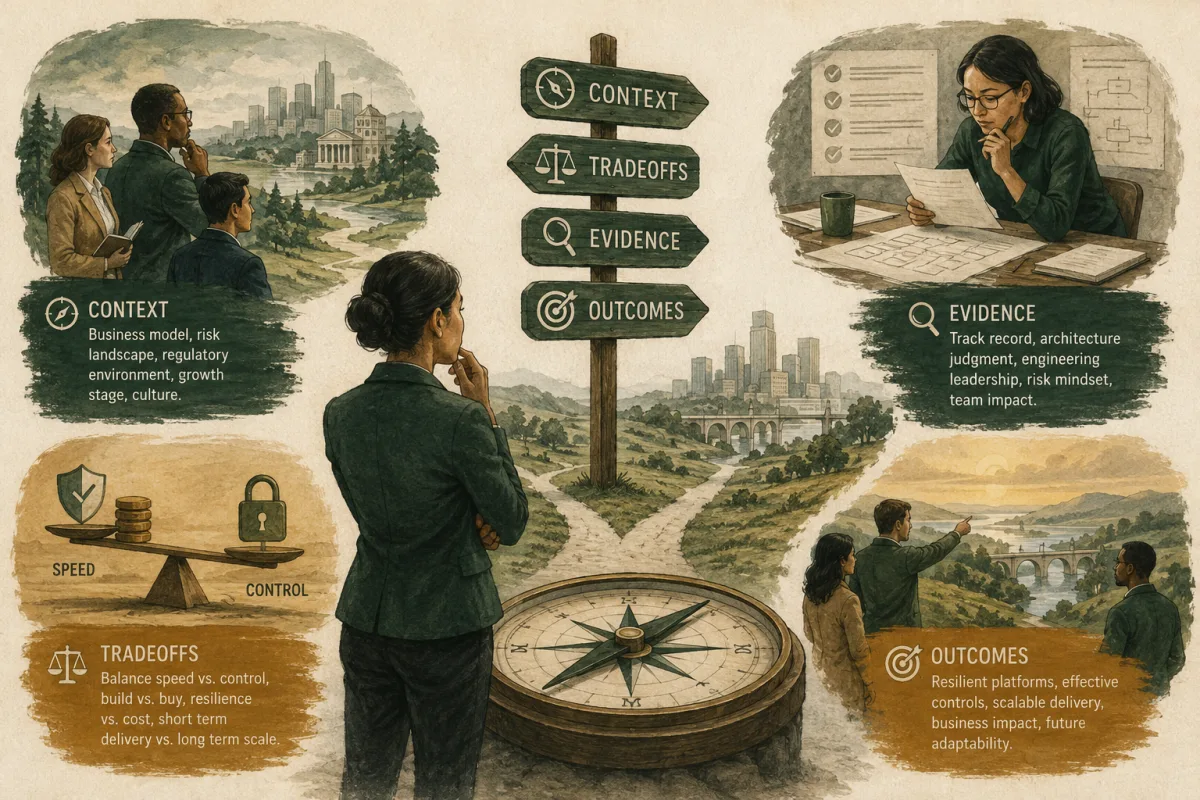
Part-time capacity can work when the company has capable execution owners, clear escalation routes and a bounded set of leadership decisions. It becomes a poor fit when the role implicitly requires continuous incident command, daily management of a large organization, extensive partner negotiations and simultaneous major platform change. Calling that workload fractional does not make it smaller.
Review the expected week with the candidate. Include preparation, leadership meetings, decision writing, team support, partner work and unplanned escalation. Identify who acts when the fractional CTO is unavailable and which events trigger an agreed response. If the answer depends on informal goodwill, the operating model is not complete.
A good fractional CTO may recommend a permanent leader, an interim full-time appointment or additional specialist capacity. Evaluate that recommendation against the work rather than treating it as a failure of the original model. The purpose is a dependable technology organization that can support its product commitments; the engagement label is secondary.
Make the board conversation decision-ready
Fintech boards do not need a catalogue of vulnerabilities or a wall of delivery metrics. They need to understand which product and technology exposures could change the plan, what management is doing, which investment or risk acceptance requires approval, and what evidence will show improvement.
A concise technology and resilience review can include:
- critical customer journeys and current service performance;
- material incidents, causes, customer impact, and completed learning;
- security and control exceptions that exceed management tolerance;
- third-party concentration and upcoming contractual decisions;
- platform constraints against the growth forecast;
- capability and leadership gaps;
- investment decisions with alternatives and consequences.
The CTO should distinguish leading signals from outcomes and clearly label uncertainty. A green dashboard built from incomplete evidence is more dangerous than an explicit unknown.
For fractional mandates, agree who represents technology between scheduled sessions and what triggers immediate escalation. Limited capacity can work when the system routes information and authority deliberately. It fails when urgent risk is discovered only at the next calendar meeting.
Frequently asked questions
What does a fintech CTO own?
A fintech CTO connects product growth with platform correctness, resilience, security, data governance, third-party risk, regulatory collaboration, team capability, and transparent technology investment.
Does a fintech CTO need compliance experience?
They need to work effectively with legal, risk, security, compliance, audit, and operations. The specific regulatory depth depends on product, license, jurisdiction, partners, and customer model.
When should a fintech hire a fractional CTO?
Fractional leadership can fit when senior technology decisions are material but bounded: pre-license preparation, enterprise readiness, platform assessment, leadership transition, diligence, resilience, or a defined scaling mandate.
How do I vet a fintech CTO?
Use scenarios involving money movement, correctness, incidents, regulated change, security evidence, data, vendors, and customer trust. Verify personal ownership and references in comparable operating contexts.
Sources and further reading
Turn research into a mandate
See the cost and hiring model before you shortlist.
Use the free calculator, then save a candidate search or post a transparent role when the mandate is ready.